Google Under Fire for Circumvention of Cookie Settings in Safari for iOS to Track Users - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Google Under Fire for Circumvention of Cookie Settings in Safari for iOS to Track Users

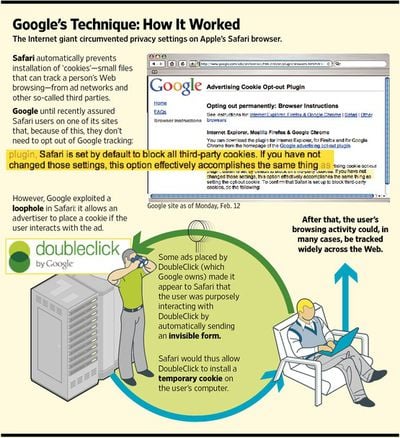
The Wall Street Journal reports that Google and several other advertising agencies have been discovered to be circumventing privacy protections in Apple's Safari browser for iOS devices in order to track users through ads on numerous popular websites. Google implemented the technique in order to embed +1 buttons on its ads, tricking users' systems into allowing cookies by using an invisible form submission to make Google's third-party cookies, which are blocked by Safari, appear as first-party cookies that are allowed.

To get around Safari's default blocking, Google exploited a loophole in the browser's privacy settings. While Safari does block most tracking, it makes an exception for websites with which a person interacts in some way—for instance, by filling out a form. So Google added coding to some of its ads that made Safari think that a person was submitting an invisible form to Google. Safari would then let Google install a cookie on the phone or computer.

The cookie that Google installed on the computer was temporary; it expired in 12 to 24 hours. But it could sometimes result in extensive tracking of Safari users. This is because of a technical quirk in Safari that allows companies to easily add more cookies to a user's computer once the company has installed at least one cookie.
google safari ios tracking
Google halted the practice once it was contacted by The Wall Street Journal about it, but has tried to downplay the impact of the issue.

In a statement, Google said: "The Journal mischaracterizes what happened and why. We used known Safari functionality to provide features that signed-in Google users had enabled. It's important to stress that these advertising cookies do not collect personal information."

In a companion blog post, The Wall Street Journal notes that the loophole that had permitted Google to bypass Safari's privacy protections has been closed in WebKit, the open source engine behind Safari, with the change having been made by two Google engineers. Consequently, Apple could and appears to be preparing to bring that fix to the public version of Safari.

An Apple spokesman said: “We are aware that some third parties are circumventing Safari’s privacy features and we are working to put a stop to it.”

An update to the software that underlies Safari has closed the loophole that allows cookies to be set after the automatic submission of invisible forms. Future public versions of Safari could incorporate that update. The people who handled the proposed change, according to software documents: two engineers at Google.

The issue was discovered by Stanford graduate student Jonathan Mayer, who has also published an extensive blog post offering additional technical details on how Google and other advertising companies circumvented Safari's default cookie settings.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

3N16MA Avatar
190 months ago
"Don't be evil."
Score: 36 Votes (Like | Disagree)
190 months ago
This is completely unacceptable. You would expect this kind of behavior from some type of shady malware outfit. Is this what Google has become? I know the "don't be evil" thing was thrown out the window a long time ago but this is stooping to a new low even for Google.
Score: 32 Votes (Like | Disagree)
lifeinhd Avatar
190 months ago
It's like Google is trying to become nothing more than adware or something.

:rolleyes:
Score: 31 Votes (Like | Disagree)
190 months ago
If they behave in this way with someone else's browser, makes you wander what shady activities they get up to on their own.
Score: 30 Votes (Like | Disagree)
FloatingBones Avatar
190 months ago
This is evil.

This is evil. These yahoos were deliberately working around the privacy/security on a platform. There should be a massive fine and people should be fired from the company.

The really shocking thing is that very smart people within the company noted this loophole and designed the workaround. Did their ethical light-bulbs never go on? Can the government subpoena email records to see how high up the company people knew about this evil act?
Score: 30 Votes (Like | Disagree)
trainwrecka Avatar
190 months ago
Google exploits it.
Google fixes it (both on their end, and in Webkit project source)

Sounds like it really was purely unintentional. It's such a short lived behavior, they can't really get anything significant out of it.

Non-issue, only newsworthy because it's mildly interesting.

Yup, I "unintentionally" write lines of code all the time that exploit loopholes that benefit me.
Score: 29 Votes (Like | Disagree)













