Security Firm Symantec Analyzes the Profitability of the OSX.Flashback Botnet - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Security Firm Symantec Analyzes the Profitability of the OSX.Flashback Botnet

filevaultSecurity firm Symantec previously estimated that the authors of the Flashback malware that affected hundreds of thousands of Macs at its peak could have been generating up to $10,000 per day by hijacking users' ad clicks. Further analysis from the company suggests that the developers may have only earned $14,000 over the three weeks the malware was active.

From our analysis we have seen that, for a three-week period starting in April, the botnet displayed over 10 million ads on compromised computers but only a small percentage of users who were shown ads actually clicked them, with close to 400,000 ads being clicked. These numbers earned the attackers $14,000 in these three weeks, although it is worth mentioning that earning the money is only one part of the puzzle—actually collecting that money is another, often more difficult, job. Many PPC providers employ anti-fraud measures and affiliate-verification processes before paying. Fortunately, the attackers in this instance appear to have been unable to complete the necessary steps to be paid.

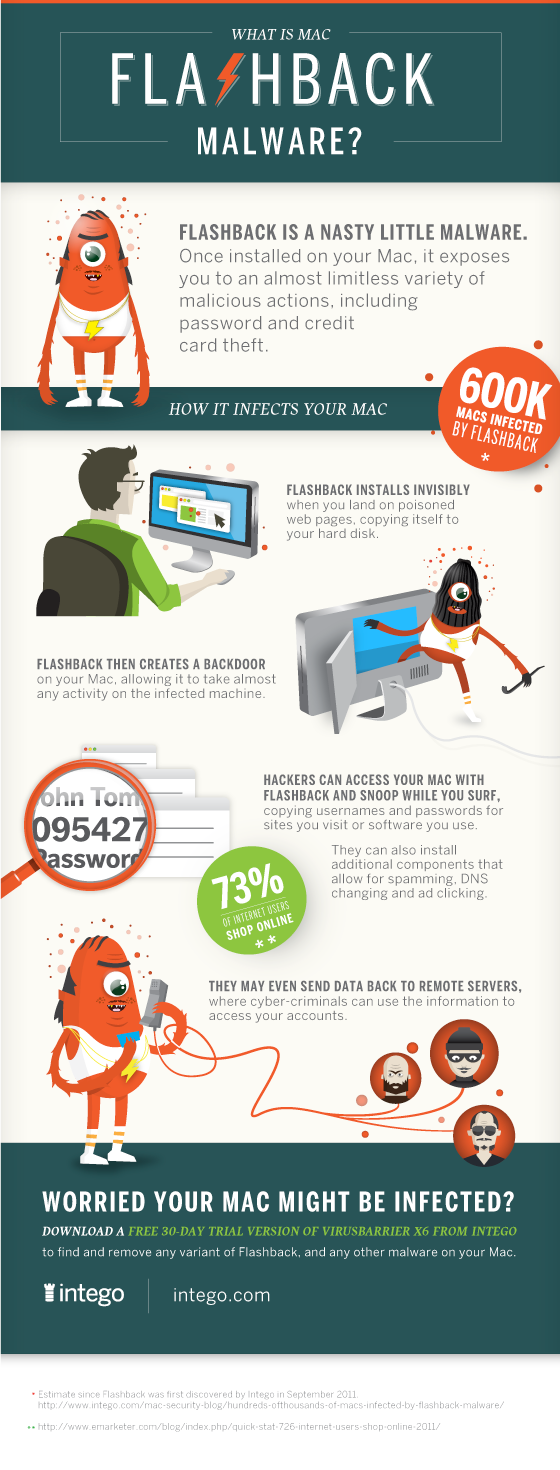
It is estimated the actual ad-clicking component of Flashback was only installed on about 10,000 of the more than 600,000 infected machines. In other words, utilizing less than 2% of the entire botnet the attackers were able to generate $14,000 in three weeks, meaning that if the attackers were able to use the entire botnet, they could potentially have earned millions of dollars a year.

Symantec notes that the malware developers displayed more than 10 million hijacked ads and could have delivered many more if the developers had been more successful in their attacks.

Some security specialists have said that the Mac OS is "really vulnerable" to further infections, though these claims should perhaps be taken with a grain of salt -- those security specialists make their living off vulnerabilities and it is in their best interest to promote awareness of them.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

187 months ago
those security specialists make their living off vulnerabilities, and it is in their best interest to promote awareness of them.

I'll say. The more afraid we are, the more we'll pay for their placebo security software.

I say the best security is knowing how to avoid infections in the first place. If you can learn not to download mysterious files, you're half way there.
Score: 8 Votes (Like | Disagree)
gnasher729 Avatar
187 months ago
I wish I made $14,000 in 3 weeks :(
Your maths is wrong.

This isn't one person making $14,000 profit for three weeks of work. There is a lot more work than three weeks of hacking, with many more people involved, for a scheme that managed to produce $14,000 in revenue for three weeks and then fizzled out. A complex software project producing a total of $14,000 in revenue.

I did a quick calculation using the total annual revenue of my company and the number of developers employed, using a number of 230 working days, and I couldn't spend more than three or four days of work for one developer for $14,000 revenue.

I wouldn't be surprised if websites like macrumors did get more additional ad revenue due to people reading stories about flashback and clicking on ads on macrumors, than these hackers made.

PS. Seems at least one of those hackers was angry because I told them they are stupid and doing a lot of work for very little money.
Score: 6 Votes (Like | Disagree)
Diode Avatar
187 months ago
Thanks StrikerShoot, I love a good infographics, but I have a good understanding of the threats Malware poses, and likewise the criminal mind behind a hacker. I'm thinking Godfather 3 style, going legit.

I was thinking without all the malicious aspects, voluntary opt-in Adnets where you technically farm all their clicks, think of it as an investment opportunity with micro returns. Micro input, micro returns. Still returns!

It sounds heaps like a scheme/existing web advertising but with the user opted-in, subscription based system.

A lot of malware / phishing scams are run by organized crime in Russia.
Score: 5 Votes (Like | Disagree)
187 months ago
No way

It would be a cold day in hell before I would ever buy a Symantec product for mac. Their PC editions are resource killing crap. I would put MSE up against them any day.
Score: 4 Votes (Like | Disagree)
187 months ago
This has got to be a business model right.

Ad-hijacking. Earn heaps through people clicking on Ads, invest, profit, repay people.

Considering how Flashback infects Macs, seems like a hackers' basic business model to me..

MacRumors content image
Score: 4 Votes (Like | Disagree)
gnasher729 Avatar
187 months ago
I'm waiting for the next story about how an antivirus software update goes bad and destroys the system. Those are always fun to hear about.

That was yesterday. Does that count as "the next story"? Headline: "'Catastrophic' Avira antivirus update bricks Windows PCs"

http://www.theregister.co.uk/2012/05/16/avira_update_snafu/

This "anti-virus" software thought it had found viruses in essential parts of Windows, that are actually signed by Microsoft. Someone commented "Either the bad guys cracked Microsoft's code signing; in that case we can just give up. Or they didn't, in that case the anti-virus software was wrong. In either case, the anti-virus software shouldn't touch anything that is code-signed by Microsoft".
Score: 3 Votes (Like | Disagree)