New U.S. Guidelines Could Halt Use of SMS for Two-Factor Authentication - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

New U.S. Guidelines Could Halt Use of SMS for Two-Factor Authentication

The US National Institute for Standards and Technology has released a new draft of its Digital Authentication Guideline, which sets the rules that all authentication software eventually follows. In the document, NIST deprecates the implementation of SMS as a method with which users validate a second level of security on various accounts, "no longer" allowing its use in future guidelines as it is considered not secure enough (via TechCrunch).
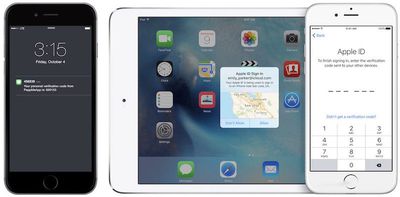
iOS two-factor authentication

Two-factor authentication via SMS (left) and an alternative trusted iOS device (right)

Setting up two-factor authentication through text messages is one of the most popular ways users add another layer of security onto an account, on top of a basic password, including those for Apple's own software, like Apple ID and iCloud. Other than SMS, Apple allows users to implement two-factor authentication through a simple push notification sent to another "trusted device," or a phone call.

If the out of band verification is to be made using a SMS message on a public mobile telephone network, the verifier SHALL verify that the pre-registered telephone number being used is actually associated with a mobile network and not with a VoIP (or other software-based) service. It then sends the SMS message to the pre-registered telephone number. Changing the pre-registered telephone number SHALL NOT be possible without two-factor authentication at the time of the change. OOB using SMS is deprecated, and will no longer be allowed in future releases of this guidance.

The new guidelines also make a point for companies to ensure that two-factor authentication notifications aren't going through a VoIP service, which could be easily compromised. NIST also includes "limited use" of biometrics as a way for users to gain access to their second layer of authentication, meaning Apple could pivot to Touch ID as an alternative if SMS support for the security feature officially comes to an end.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

132 months ago
I thought our government was trying to weaken security so they can access our phones. Who at NIST made this mistake of proposing a verification process that was more secure? Probably fired by the end of the week. :eek::D:p:cool:
Score: 20 Votes (Like | Disagree)
John Mcgregor Avatar
132 months ago
Apple can send an iMessage.
Score: 10 Votes (Like | Disagree)
gwhizkids Avatar
132 months ago
But its a much better way than doing nothing at all. Personally, we need to get to a whole new paradigm of authentication, period. Deprecate the password!
Score: 7 Votes (Like | Disagree)
Iconoclysm Avatar
132 months ago
I thought our government was trying to weaken security so they can access our phones. Who at NIST made this mistake of proposing a verification process that was more secure? Probably fired by the end of the week. :eek::D:p:cool:
If the government convinces you to use TouchID, they can force you to unlock your phone without a PIN.
Score: 6 Votes (Like | Disagree)
big-ted Avatar
132 months ago
Good.

SMS is a piss poor way of doing 2FA and lazy companies need to move towards apps such as google authenticator, authy, e.g.
You are assuming that everyone on the planet has a smart phone
Score: 5 Votes (Like | Disagree)
132 months ago
While it may not be perfect, the suggestion everyone should use an app eliminates any two factor authentication for small companies /developers who may not have those resources starting out. Instead of deprecating SMS, which is better than nothing, why not recommend it as a last resort?
Score: 5 Votes (Like | Disagree)