Bypass Flaw in Newly Released macOS Mojave Update Lets Hackers Access Protected Files - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Bypass Flaw in Newly Released macOS Mojave Update Lets Hackers Access Protected Files

Researcher Patrick Wardle, who has uncovered many security flaws in Apple's macOS operating system, today shared some details on a new vulnerability that he's found in the newly released macOS Mojave update.

As outlined by BleepingComputer, Wardle discovered that he was able to access Contacts data from the address book using an unprivileged app, as demonstrated in the video below.


According to Wardle, the vulnerability is a result of the way that Apple implemented new macOS privacy protections in the Mojave update.

"I found a trivial, albeit 100% reliable flaw in their implementation," he told us, adding that it allows a malicious or untrusted app to bypass the new security mechanism and access the sensitive details without authorization.

The bypass does not work with all of the new privacy protection features in macOS Mojave, and hardware-based components, such as the webcam, are not affected. Full details on the vulnerability are not available yet, as Wardle plans to share technical details in November.

In the macOS Mojave update, Apple made a change that requires explicit user consent for apps to access location data, camera, contacts, calendars, reminders, messages history, Safari data, mail databases, and other sensitive data, which should prevent the vulnerability that Wardle demonstrates.
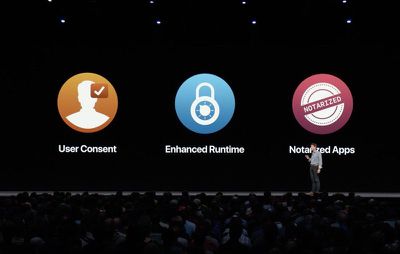
macosmojaveprivacy
Apple will undoubtedly address the security flaw discovered by Wardle in an upcoming update to macOS Mojave.


Related Forum: macOS Mojave

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

SecuritySteve Avatar
104 months ago
As a security researcher professional, this is entirely inappropriate. He should have contacted Apple during the beta release cycle and gotten it fixed. If Apple needs more time to fix it, and is aware of the issue, then you keep the vulnerability under wraps so that other hackers do not exploit your vulnerability while it has no fix.

The only reason to publish a vulnerability with no fix is if the vendor WILL NOT FIX the vulnerability. I doubt that is the case here. This Wardle is seeking attention, and should be looked down upon.

See the guys listed here? These are the true professionals, they did it right.

https://support.apple.com/en-us/HT209139
Score: 52 Votes (Like | Disagree)
fokmik Avatar
104 months ago
why come forward today and not earlier that Apple can fix this before Mojave release ? i wonder...
Score: 31 Votes (Like | Disagree)
dannyyankou Avatar
104 months ago
Why dont they do proper testing?
Yeah they should have a beta program or something with a feedback app, then this would’ve been discovered months ago :rolleyes:
Score: 24 Votes (Like | Disagree)
rafark Avatar
104 months ago
Why dont they do proper testing? A bit embarrassing for a trillion dollar company.
Score: 21 Votes (Like | Disagree)
dannyyankou Avatar
104 months ago
It requires the Mac to be unlocked in the first place, so this isn’t the worst security flaw in the world.
Score: 11 Votes (Like | Disagree)
MacDawg Avatar
104 months ago
Oh goodie, now we can have all of the usual suspects flock here to take a **** on Apple
Score: 10 Votes (Like | Disagree)