Apple Ups Bug Bounty Payouts, Expands Access to All Researchers and Launches macOS Program - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Apple Ups Bug Bounty Payouts, Expands Access to All Researchers and Launches macOS Program

Apple is introducing an expanded bug bounty program that covers macOS, tvOS, watchOS, and iCloud as well as iOS devices, Apple's head of security engineering Ivan Krstić announced this afternoon at the Black Hat conference in Las Vegas.

Apple introduced its bug bounty program for iOS devices in August of 2016, allowing security researchers who locate bugs in iOS to receive a cash payout for disclosing the vulnerability to Apple. Prior to now, non-iOS devices were not included, a move that has previously been criticized by the security community.
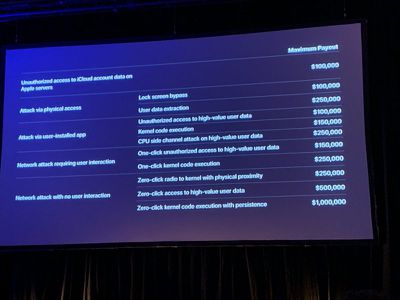
applebugbountypayouts
Apple's lack of a macOS bug bounty program made headlines earlier this year when a German teenager initially refused to hand over details of a major macOS Keychain security flaw because Apple didn't have a payout. While he did ultimately provide the info to Apple, he said that he hoped his refusal would inspire Apple to expand its bug bounty program, which the company has indeed done.

With the launch of the new macOS bug bounty program, Apple is opening its bug bounties up to all researchers later this year and it is increasing the maximum size of the bounty from $200,000 per exploit to $1 million depending on the nature of the security flaw. A zero-click kernel code execution with persistence will earn the maximum amount.

Researchers who discover vulnerabilities in pre-release software before general release can qualify for up to a 50 percent bonus payout on top of the base bug bounty amount.

As reported earlier this week, Apple also plans to provide vetted and trusted security researchers and hackers with "dev" iPhones, aka special iPhones that provide deeper access to the underlying software and operating system that will make it easier for vulnerabilities to be discovered.
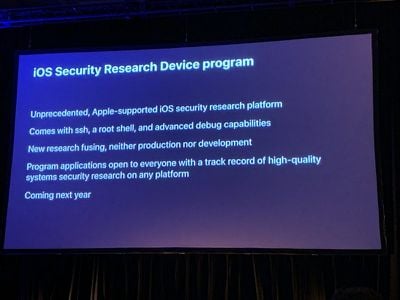
appleresearchdeviceprogram
Apple is providing these iPhones as part of its new iOS Security Research Device Program, launching next year. Apple's aim with these new bug bounty efforts is to encourage additional security researchers to disclose vulnerabilities, ultimately leading to more secure devices for consumers.

(Thanks, SecuritySteve!)

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

smithrh Avatar
93 months ago
Overdue, but a good move.
Score: 17 Votes (Like | Disagree)
IIGS User Avatar
93 months ago
This is welcome news. It would be nice if Apple could fully secure its own software but that's just not how the industry works.
There's an old saying I'll paraphrase. "No plan of battle survives first contact with the enemy".

No software testing can put every piece of software into every possible configuration. One different application, combined with a different time zone, and a screen configuration can change things enough for something inside to cry "uncle".

Just like my old man used to say. Never buy the first year of a new model car or truck. Give it a year or two for some other idiot to find out the wiper switch doesn't like prune fumes, or some other issue no one thought up....
Score: 11 Votes (Like | Disagree)
93 months ago
apple probably figured its cheaper to have someone look for bugs than hiring a team of engineers.
Also, there are legal issues if an Apple engineer reverse engineers third-party apps on their platform and looks at their code, to use as part of an attack. This could lead to accusations that Apple copied from third parties' code, something that independent researchers don't run into.
Score: 6 Votes (Like | Disagree)
93 months ago
apple probably figured its cheaper to have someone look for bugs than hiring a team of engineers.
Highly doubt that — Just more eyes looking. Apple is secretive, not cheap. They have an information-sharing issue.
Score: 6 Votes (Like | Disagree)
93 months ago
Hackers are now called "researchers".
Score: 5 Votes (Like | Disagree)
Justanotherfanboy Avatar
93 months ago
time to get PAID
Lol, you have a zero-click kernel code execution with persistence bug you found, that you’ve been sitting on???
By all means, sir.... GET PAID!
Score: 3 Votes (Like | Disagree)