Apple Online Store Security Flaw Exposed PINs of T-Mobile Customers - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Apple Online Store Security Flaw Exposed PINs of T-Mobile Customers

A security flaw in Apple's online store exposed the account PINs of more than 72 million T-Mobile customers, reports BuzzFeed News.

The vulnerability was discovered by security researchers Phobia and Nicholas "Convict" Ceraolo, who also found a similar flaw in the website for phone insurance company Asurion that exposed AT&T account PINs.

Both Apple and Asurion fixed the website flaws that left the PINs vulnerable after learning about them from BuzzFeed News. Apple opted not to provide further comment on the situation, but told BuzzFeed News that it is "very grateful to the researchers who found the flaw."
tmobileapplepage

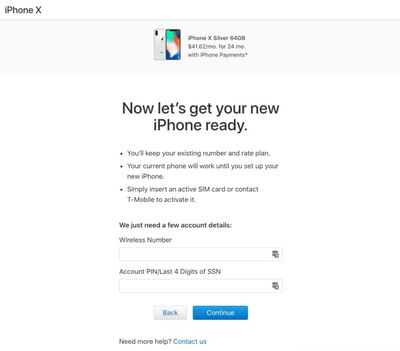
The page on Apple's site that let hackers brute force PINs, via BuzzFeed News

PINs, or passcodes, are numbers that are used as an additional account security measure by many carriers in the United States. Mobile device PINs are typically a last line of defense for a cellular account as both carrier websites and support staff will ask for the PIN for confirmation before making account changes.

SIM hacking, which uses social engineering to get carrier support staff to transfer a person's phone number to a new SIM, has become increasingly prevalent due to the number of accounts (bank, email, social media, etc.) that are tied to a person's phone number. A PIN is used as a defense mechanism against SIM hacking, which means exposed PINs can be particularly dangerous.

Accessing the T-Mobile PINs on Apple's website involved a brute force attack where a hacker used software to input multiple different numeric combinations to guess the proper one.

As BuzzFeed News explains, after initiating a T-Mobile iPhone purchase on the Apple online store and selecting monthly payment options through T-Mobile, Apple's site directs users to an authentication form asking for a T-Mobile number and account PIN or last four digits of a social security number (which most carriers use in place of a PIN when one has not been set).

The page allowed for infinite entry attempts into the PIN field, enabling the brute force attack that let hackers guess PINs associated with a T-Mobile phone number.

The security vulnerability appears to have been limited to T-Mobile accounts, as the same validation page for other carriers on Apple's site uses a rate limit that locks access to the form for 60 minutes after five to 10 incorrect entries. Given that the other carrier pages had rate limiting enabled, it's likely Apple made an error on the T-Mobile page.

According to Ceraolo, the vulnerability is likely due to an engineering mistake made when connecting T-Mobile's account validation API to Apple's website.

A similar vulnerability on Asurion's website exposed an unspecified number of AT&T account PINs. An AT&T spokesperson said that it is working with Asurion to investigate the issue and will "take any additional action that may be appropriate."

A phone number was required for both of these attacks, limiting the number of people who may have been impacted, but AT&T and T-Mobile customers who are concerned about their account safety should choose a new PIN.


Tags: AT&T, T-Mobile

Popular Stories

iOS 28 AI

Apple Taking New Approach to Developing iOS 28 and macOS 28

Sunday November 8, 2026 7:42 am PST by
Apple has made a change to its development process for iOS 28, macOS 28, and corresponding software updates, according to Bloomberg's Mark Gurman. In his Power On newsletter today, he said Apple separates development of each year's new operating systems into three major stages. Typically, he said each stage consists of four weeks of coding followed by a four-week "convergence" period where...
duo aquarium

More Fun iPhone Duo Apps: 30 New Picks to Try

Friday November 6, 2026 3:27 pm PST by
When the iPhone Duo launched, we shared a list of some of the fun apps developers created for the new form factor. Two weeks out, developers are continuing to come up with fresh ideas, so we thought we'd share some of our favorites. Games Marbles Unhinged ($2.99) - Marbles Unhinged is a marble maze designed for the Duo. When you fold it, the floor turns into a ramp. If you stand the top...
apple pro tell logo

Apple Launching Five New Products Today

Thursday November 5, 2026 12:59 am PST by
Apple is launching five new products on Friday, November 6, following pre-orders that opened last week, including its first touchscreen MacBook Pro models. The following new products will be available from today: iPad mini with OLED display and A20 Pro chip iMac with M6 chip 14-inch MacBook Pro with M6 chip 14-inch MacBook Pro with OLED touchscreen 16-inch MacBook Pro with OLED...

Top Rated Comments

107 months ago
But forum members told me that Apple had the best security. Well except for those times when they didn't. Like the root password gate where you didn't have to put a password in to gain root access.
Score: 41 Votes (Like | Disagree)
107 months ago
But forum members told me that Apple had the best security. Well except for those times when they didn't. Like the root password gate where you didn't have to put a password in to gain root access.
Having the best security =/= flawless security. No tech company is completely flawless. But go ahead and chastise Apple for not being absolutely perfect, because that's so productive.
Score: 24 Votes (Like | Disagree)
Doctor Q Avatar
107 months ago
Four digits isn't a very long PIN. Even if the software now locks access to the form for 60 minutes after five to 10 incorrect entries, it doesn't block the exploit, just slow it down.


It seems to me that a bot could try 10 guesses for one phone number, which would lock the form for that phone number, then immediately switch to another phone number. If the phone number is locked for the IP address, it could use another IP address too.

If so, let's try a little math here: Rather than a bot trying one phone number and 10,000 different PINs in rapid succession to break it, it could try five to ten PINs for every phone number it's working on in the first hour, then try another five to ten PINs for every phone number in the second hour, and so on. In as few as 42 days it could crack every phone number. If it was trying to crack 10,000 phone numbers, it would succeed on an average of 238 phone numbers per day. That's still pretty vulnerable.
Score: 17 Votes (Like | Disagree)
mi7chy Avatar
107 months ago
Apple don't care about security because even after several security incidents customers are brain washed into thinking Apple is flawless.
Score: 10 Votes (Like | Disagree)
zakarhino Avatar
107 months ago
Security issue after security issue for T-Mobile and many carriers in general. Remember when T-Mo Germany said they don't need to salt their passwords because their security is "that good"? Or when it was discovered that it's very easy to get access to a T-Mo account AND clone people's sims because T-Mo doesn't have very good security practices beyond asking for the last 4 of your SSN? I've heard stories of people phoning up carriers under the guise of being a store employee and they get access to all sorts of information without thorough identity verification!

I know Apple are the guys that purportedly screwed up here but when you look at T-Mobile's security in general, it doesn't have a very good track record, it should have never been possible for the Tmo verification API to allow unlimited requests without a time limit. These carriers need to seriously update their security practices. Just accepting the last 4 digits of your social security number is no longer a viable option.
Score: 8 Votes (Like | Disagree)
Apple_Robert Avatar
107 months ago
Even though the fix is in place, I went ahead and changed my PIN again.

Things like this are frustrating. At the same time, most of us informed nerds and geeks realize that any time one creates an account online, there are security risks. As noted earlier, nothing in the tech world is 100% safe forever.
Score: 6 Votes (Like | Disagree)
Latest Stories
macOS 27.2.1 Fixes eMudhra Certificate Flaw in Command-Line Tools
23 minutes ago
Anthropic Launches Claude Fable 5.2 and Mythos 5.2
1 hour ago
Apple Releases macOS Golden Gate 27.2.1
3 hours ago
Apple Releases iOS 27.2.1 With Bug Fixes
3 hours ago
Apple Releases watchOS 27.2.1 and visionOS 27.2.1 With Security Fixes
3 hours ago
Apple Watch Ultra 4 Gets $99 Amazon Discounts, Starting at $699.99
3 hours ago
Apple Pay Ad Features Martial Arts Convenience Store Food Fight
3 hours ago
Apple Continues to Say Some AI Features Will Have Fees for Extra Usage
3 hours ago
Apple Announces Türkiye Expansion Plans as Tim Cook Visits
4 hours ago
Singapore Saved Apple $2.7 Billion in Taxes This Year
4 hours ago
Apple Music's 2026 Artist of the Year is Olivia Dean
5 hours ago
This Could Be Your Last Chance to Pre-Order the HomeView at a Discount
5 hours ago
Some HomePod Mini 2 Buyers Returning Units Over Mac Speaker Issues
5 hours ago
MacBook Pro With PROLED XDR Display: Details You Might Have Missed
5 hours ago
Satechi Offers MacRumors Readers 30% Off Select Accessories in Early Black Friday Sale
6 hours ago
Leaker Envisions a Shorter iPhone With a New iOS Layout
6 hours ago
Apple to Give You More Control Over When Your Mac Passwords Lock
7 hours ago
Siri Is Getting a Better Memory
8 hours ago
iPhone 18e Could Feature Bigger Display and Battery
8 hours ago
Apple's Siri Boss May Leave - Here's Who Could Take Over
8 hours ago
Apple Launching Two More New Products This Friday
9 hours ago
Apple Store Subscription Sign-Up Controversy Exposed
17 hours ago
Siri AI Rumored to Become 'More Like an Agent' as Early as Next Year
1 day ago
Apple Taking New Approach to Developing iOS 28 and macOS 28
1 day ago
Early Apple Black Friday Deals on Apple Watch, MacBook Air, and More
2 days ago
'Backglow' Lets You Customize New MacBook Pro's Glowing Apple Logo
2 days ago
Top Stories: Apple Product Launches, iOS 27.3 Beta, and More
2 days ago
More Fun iPhone Duo Apps: 30 New Picks to Try
3 days ago
Hands-On With Apple's New OLED Touchscreen MacBook Pro
3 days ago
Apple Store With All-New Design Opening Soon in Southern California
3 days ago








































