Apple to Fix macOS Mail Vulnerability That Leaves Text of Some Encrypted Emails Readable - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Apple to Fix macOS Mail Vulnerability That Leaves Text of Some Encrypted Emails Readable

There's a vulnerability in the macOS version of the Apple Mail app that leaves some of the text of encrypted emails unencrypted, according to a report from IT specialist Bob Gendler (via The Verge).

According to Gendler, the snippets.db database file used by a macOS function that offers up contact suggestions stores encrypted emails in an unencrypted format, even when Siri is disabled on the Mac.
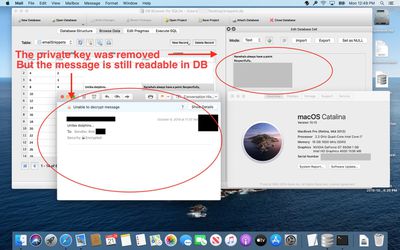
mailencryptionissue

In this email, Gendler demonstrates that the private key has been made unavailable in Mail, rendering the message unreadable. It continues to be available in the database, though.

Gendler initially discovered the bug on July 29 and reported it to Apple. Over the course of several months, Apple said that it was looking into the issue, though no fix ever came. The vulnerability continues to exist in macOS Catalina and earlier versions of macOS dating back to macOS Sierra.

Let me say that again... The snippets.db database is storing encrypted Apple Mail messages...completely, totally, fully -- UNENCRYPTED -- readable, even with Siri disabled, without requiring the private key. Most would assume that disabling Siri would stop macOS from collecting information on the user. This is a big deal.

This is a big deal for governments, corporations and regular people who use encrypted email and expect the contents to be protected. Secret or top-secret information, which was sent encrypted, would be exposed via this process and database, as would trade secrets and proprietary data.

Apple told The Verge that it has been made aware of the issue and will address it in a future software update. Apple also said that only portions of some emails are stored, and provided Gendler with instructions on preventing data from being stored by the snippets database.

This issue affects a limited number of people in practice, and is not something that macOS users should generally worry about. It requires customers to be using macOS and the Apple Mail app to send encrypted emails. It does not impact those who have FileVault turned on, and a person who wanted to access the information would also need to know where in Apple's system files to look and have physical access to a machine.

Still, as Gendler points out, this particular vulnerability "brings up the question of what else is tracked and potentially improperly stored without you realizing it."

Those concerned about this issue can prevent data from being collected in the snippets.db database by opening up System Preferences, choosing the ‌Siri‌ section, selecting ‌Siri‌ Suggestions & Privacy, choosing Mail and then turning off "Learn from this App." This will stop new emails from being added to snippets.db but won't remove those that have already been included.

Apple told The Verge that customers who want to avoid unencrypted snippets being read by other apps can avoid giving apps full disk access in macOS Catalina. Turning on FileVault will also encrypt everything on the Mac.

Full details on the vulnerability can be read in Gendler's Medium article.

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

90 months ago

Apple has so many bugs now. What a shame. They’re all marketing now
Don't worry Tim's on the case...

Season 2 of The Morning Show will feature 20% more Apple logos.
Score: 17 Votes (Like | Disagree)
Dovydas Avatar
90 months ago

This is overblown. S/MIME = HTTPS for e-mail. Encryped webpages are cached and indexed all the time.

Bob Gendler is acting like S/MIME is some super-high security protocol where it isn't. It doesn't protect "Secret or top-secret information".
The point is if you do something do it properly. What else is overblown by your definition? It is just bad attitude to have period.
Score: 14 Votes (Like | Disagree)
90 months ago

Who doesn't have FileVault turned on???
Me.
Score: 12 Votes (Like | Disagree)
SDJim Avatar
90 months ago
Who doesn't have FileVault turned on???
Score: 9 Votes (Like | Disagree)
jasnw Avatar
90 months ago
Given Apple's track record on fixing Mail problems I'd not expect this to be fixed until, well, ever?
Score: 6 Votes (Like | Disagree)
90 months ago

You missed my point. As I said, we index and cache encrypted webpages all the time for user features.
This is a false equivalence. Unless you actually break the end-to-end encryption (e.g. by forcing the user to accept a new root certificate), you can only index encrypted web page content that is accessible without prior authentication. Encrypted email should *never* be readable by anyone but the addressee, neither in transit nor at rest.

This is absolutely a big deal in corporate environments. Full disc encryption is not a replacement, since e.g. it might be decryptable to admins who should not have access to another employee's protected emails.
Score: 6 Votes (Like | Disagree)