Security Researcher Shows Off Now-Fixed macOS Hack That Used Microsoft Office - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

Security Researcher Shows Off Now-Fixed macOS Hack That Used Microsoft Office

macOS users could be targeted with malicious attacks using Microsoft Office files that have macros embedded, according to details on the now-fixed exploit shared today by security researcher Patrick Wardle, who also spoke to Motherboard.
microsoftofficemacromacexploit
Hackers have long used Office files with macros embedded in them as a way to get access to Windows computers, but the exploit is also possible on macOS. According to Wardle, a Mac user could potentially be infected just by opening a Microsoft Office file that has a bad macro in it.

Wardle shared a blog post on the exploit that he found for manipulating Office files to impact Macs, which he's highlighting during today's online Black Hat security conference.

Apple fixed the exploit that Wardle used in macOS 10.15.3, so that particular vulnerability is no longer available for hackers to use, but it offers an interesting look at an emerging method of attack that we could see more of in the future.

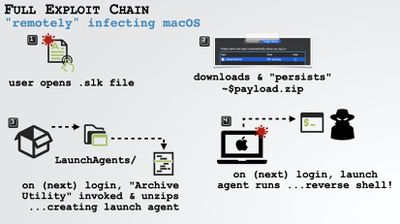
Wardle's hack was complicated and involved multiple steps, so those interested in full details should read his blog, but basically he used an Office file with an old .slk format to run macros on macOS without informing the user.

"Security researchers love these ancient file formats because they were created at a time when no one was thinking about security," Wardle told Motherboard.

After using the antiquated file format to get macOS to run a macro in Microsoft Office without letting the user know, he used another flaw that let a hacker escape the Microsoft Office Sandbox with a file that uses a $ sign. The file was a .zip file, which macOS didn't check against the notarization protections that prevent users from opening files not from known developers.

A demonstration of a downloaded Microsoft Office file with a macro being used to open up Calculator.

The exploit required the targeted person to log in to their Mac on two separate occasions as logins trigger different steps in the exploit chain, which makes it less likely to happen, but as Wardle says, only one person needs to fall for it.

Microsoft told Wardle that it has found that "any application, even when sandboxed, is vulnerable to misuse of these APIs," and that it is in contact with Apple to identify and fix issues as they arise. The vulnerabilities that Wardle used to demonstrate how macros can be abused have long since been patched by Apple, but there's always a chance that a similar exploit could pop up later.

Mac users are not invulnerable to viruses and should exercise caution when downloading and opening files from unknown sources, and sometimes, even known sources. It's best to stay away from suspicious Office files and other files that have shady origins, even with the protections that Apple has built into macOS.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

AngerDanger Avatar
80 months ago
You know **** got real when they break out the slab serif font.

MacRumors content image
Score: 7 Votes (Like | Disagree)
Chompineer Avatar
80 months ago

Yet another reason NOT to use M$ junk!!
Lol. Chill. Apple is guilty of plenty of faults too.
Score: 5 Votes (Like | Disagree)
coords Avatar
80 months ago
Yet another reason NOT to use M$ junk!!
Score: 5 Votes (Like | Disagree)
PlayUltimate Avatar
80 months ago
This is more of a Trojan horse than a virus; albeit, most people don't know the difference.

Note: for extra security, your Admin user should not be your daily user. I always have my family members create a Me (Standard) and Me_Admin (Admin) users when they get a computer. Just makes an extra step to get access to root directories, install apps, etc.
Score: 4 Votes (Like | Disagree)
Mr. Awesome Avatar
80 months ago

You know **** got real when they break out the slab serif font.

MacRumors content image
And check out those blood splatter icons.

And that hacker wearing a totally inconspicuous hat. And the snake eyes. That’s what real hackers look like, kids.

*Wait, what? They’re not blood icons? That’s way less exciting/terrifying.*
Score: 3 Votes (Like | Disagree)
80 months ago

The exploit required the targeted person to log in to their Mac on two separate occasions as logins trigger different steps in the exploit chain, which makes it less likely to happen
This part in the article seems wrong. The fact that the exploit requires two logins/restarts does not make it less likely to happen; it just means it might take some time until it becomes fully operational.

Wardle's original article is actually a pretty interesting read, if you have a few minutes. My favorite part is:
if the “Disable all macros without notification” setting is enabled, ironically, this macro code will be automatically executed anytime the document is opened!
Score: 2 Votes (Like | Disagree)