AirTag 'Lost Mode' Vulnerability Can Redirect Users to Malicious Websites - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

AirTag 'Lost Mode' Vulnerability Can Redirect Users to Malicious Websites

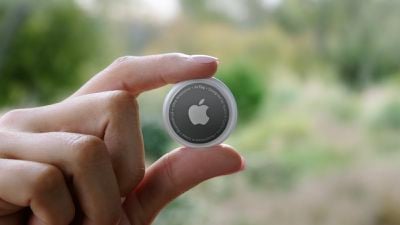
The AirTag feature that allows anyone with a smartphone to scan a lost ‌AirTag‌ to locate the contact information of the owner can be abused for phishing scams, according to a new report shared by KrebsOnSecurity.
f1618938547
When an ‌AirTag‌ is set in Lost Mode, it generates a URL for https://found.apple.com and it lets the ‌AirTag‌ owner enter a contact phone number or email address. Anyone who scans that ‌AirTag‌ is then directed automatically to the URL with the owner's contact information, with no login or personal information required to view the provided contact details.

According to KrebsOnSecurity, Lost Mode does not prevent users from injecting arbitrary computer code into the phone number field, so a person who scans an ‌AirTag‌ can be redirected to a phony iCloud login page or another malicious site. Someone who does not know that no personal information is required to view an ‌AirTag‌'s information could then be tricked into providing their ‌iCloud‌ login or other personal details, or the redirect could attempt to download malicious software.

The ‌AirTag‌ flaw was found by security consultant Bobby Raunch, who told KrebsOnSecurity that the vulnerability makes AirTags dangerous. "I can't remember another instance where these sort of small consumer-grade tracking devices at a low-cost like this could be weaponized," he said.

Rauch contacted Apple on June 20, and Apple took several months to investigate. Apple told Rauch last Thursday that it would address the weakness in an upcoming update, and asked him not to talk about it in public.

Apple did not answer his questions about whether he would receive credit or whether he qualified for the bug bounty program, so he decided to share details on the vulnerability because of Apple's lack of communication.

"I told them, 'I'm willing to work with you if you can provide some details of when you plan on remediating this, and whether there would be any recognition or bug bounty payout'," Rauch said, noting that he told Apple he planned to publish his findings within 90 days of notifying them. "Their response was basically, 'We'd appreciate it if you didn't leak this.'"

Last week, security researcher Denis Tokarev made several zero-day iOS vulnerabilities public after Apple ignored his reports and failed to fix the issues for several months. Apple has since apologized, but the company is continuing to receive criticism for its bug bounty program and the slowness with which it responds to reports.


Related Roundup: AirTag
Buyer's Guide: AirTag (Buy Now)

Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

btrach144 Avatar
65 months ago
Why is apple so lazy and incompetent when dealing with security researchers?
Score: 45 Votes (Like | Disagree)
65 months ago

Why is apple so lazy and incompetent when dealing with security researchers?
Arrogance
Score: 32 Votes (Like | Disagree)
Naraxus Avatar
65 months ago
Rofl. And Apple has the chutzpah to claim they care about & protect user privacy
Score: 26 Votes (Like | Disagree)
65 months ago
Its just sad what Apple has become. Here you have people finding vulnerabilities that the staff you pay didn't find. It's essentially like having other people on your payroll that you only have to pay if they find something. Instead they treat them like crap, ignoring simple credit, trying to hush them, or worse yet just ignoring the vulnerability. Its not like paying them would even be a blip in the billions/quarterly profit they make. Instead of encouraging people to report these thing to them, they push them away to potentially sell it to the bad guys. Hopefully it's worth the bad PR, unknown security holes, and the continued erosion of their "privacy" marketing BS.
Score: 25 Votes (Like | Disagree)
red elma Avatar
65 months ago
Vulnerability chances are greater in logging into this forum than an AirTag in 'Lost Mode'
Score: 15 Votes (Like | Disagree)
SpaceN64 Avatar
65 months ago
Well that sounds bad
Score: 15 Votes (Like | Disagree)