M1 Macs Targeted by Additional Malware, Exact Threat Remains a Mystery - MacRumorsOpen MenuShow RoundupsShow Forums menuVisit ForumsOpen Sidebar
Skip to Content

M1 Macs Targeted by Additional Malware, Exact Threat Remains a Mystery

The second known piece of malware that has been compiled to run natively on M1 Macs has been discovered by security firm Red Canary.
m1 mac mini screen
Given the name "Silver Sparrow," the malicious package is said to leverage the macOS Installer JavaScript API to execute suspicious commands. After observing the malware for over a week, however, neither Red Canary nor its research partners observed a final payload, so the exact threat that the malware poses remains a mystery.

Nevertheless, Red Canary said the malware could be "a reasonably serious threat":

Though we haven't observed Silver Sparrow delivering additional malicious payloads yet, its forward-looking M1 chip compatibility, global reach, relatively high infection rate, and operational maturity suggest Silver Sparrow is a reasonably serious threat, uniquely positioned to deliver a potentially impactful payload at a moment's notice.

According to data provided by Malwarebytes, "Silver Sparrow" had infected 29,139 macOS systems across 153 countries as of February 17, including "high volumes of detection in the United States, the United Kingdom, Canada, France, and Germany." Red Canary did not specify how many of these systems were M1 Macs, if any.

Given that the "Silver Sparrow" binaries "don't seem to do all that much" yet, Red Canary referred to them as "bystander binaries." When executed on Intel-based Macs, the malicious package simply shows a blank window with a "Hello, World!" message, while the Apple silicon binary leads to a red window that says "You did it!"
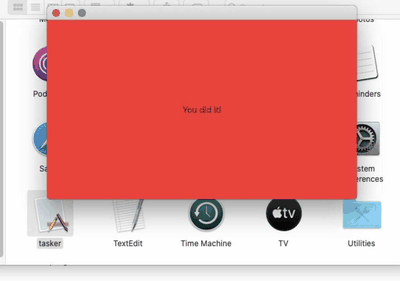
you did it silver sparrow
Red Canary shared methods for detecting a wide array of macOS threats, but the steps are not specific to detecting "Silver Sparrow":

- Look for a process that appears to be PlistBuddy executing in conjunction with a command line containing the following: LaunchAgents and RunAtLoad and true. This analytic helps us find multiple macOS malware families establishing LaunchAgent persistence.
- Look for a process that appears to be sqlite3 executing in conjunction with a
command line that contains: LSQuarantine. This analytic helps us find multiple macOS malware families manipulating or searching metadata for downloaded files.
- Look for a process that appears to be curl executing in conjunction with a command line that contains: s3.amazonaws.com. This analytic helps us find multiple macOS malware families using S3 buckets for distribution.

The first piece of malware capable of running natively on M1 Macs was discovered just days ago. Technical details about this second piece of malware can be found in Red Canary's blog post, and Ars Technica has a good explainer as well.


Popular Stories

iOS 27 Next to iPhone

Here's When iOS 27 Rolls Out Today in Every Time Zone [Update: It's Out]

Sunday September 13, 2026 3:00 am PDT by
Update 10:04 a.m.: iOS 27 is rolling out now, though it may take a bit for all users to see it, so keep checking! Apple is about to release iOS 27, which will finally deliver more advanced Siri AI capabilities as well as a variety of other refinements, improvements, and new features to iPhones. It's Apple's biggest software update of the year, and Apple announced at Wednesday's iPhone event...
iOS 27 Icon iPhone

iOS 27 Available Now With These 8 New Features

Monday September 14, 2026 9:00 am PDT by
Update — 10 a.m. Pacific Time: Apple has released iOS 27. During its iPhone 18 Pro and iPhone Duo event last week, Apple announced that iOS 27 will be released widely on Monday, September 14. iOS 27 should be available around 10 a.m. Pacific Time / 1 p.m. Eastern Time today via the Settings app, under General → Software Update. Below, we have highlighted eight new features and...
Apple iCloud Plus expansion hero

iCloud+ Now Includes Apple TV, Apple Arcade, and Curated Apple Music Stations in Over 100 Countries

Tuesday September 15, 2026 1:43 am PDT by
Apple today announced a new subscription initiative that turns paid iCloud+ subscriptions into a broader services bundle in more than 100 countries. In select countries, Apple says every paid iCloud+ plan, including the cheapest 50GB tier, now includes Apple TV and Apple Arcade "at no additional cost," while family sharing extends the storage, TV and Arcade access to up to five people....

Top Rated Comments

Vol Braakzakje Avatar
73 months ago
it’s Intel that tries to get people afraid to buy M1s
Score: 22 Votes (Like | Disagree)
73 months ago

Nothing more than fear mongering. These are just existing Mac malware/adware exploits that are being ported to run on ARM. So, what? What would you expect? All this crap comes from Windows/x86/PCs to begin with. And then MR gives is front page status? It's the same stuff that ALREADY EXISTS on other Macs and Windows PCs, for crying out loud! Click bait. Boo.
Because it’s nice to hear that more developers are porting to Apple Silicon.

It’s a feel-good article.
Score: 14 Votes (Like | Disagree)
73 months ago

Nothing more than fear mongering. These are just existing Mac malware/adware exploits that are being ported to run on ARM. So, what? What would you expect? All this crap comes from Windows/x86/PCs to begin with. And then MR gives is front page status? It's the same stuff that ALREADY EXISTS on other Macs and Windows PCs, for crying out loud! Click bait. Boo.
If security researchers say it's a big deal, it's a big deal. Why so defensive anyway?
Score: 14 Votes (Like | Disagree)
CmdrLaForge Avatar
73 months ago
Ok, how does this article help in avoiding the threat or detecting it. How does one get infected?
Score: 10 Votes (Like | Disagree)
Populus Avatar
73 months ago
Well, color me concerned.

Is this threat capable of infecting without our consent? (This is, allowing privileges when it tries to install itself). You know, requiring us to put the system password when required. Because otherwise, we should be safe just installing only from well known sources. Or Open Source software.

By the way thank you MacRumors (@Joe Rossignol, @arn) for letting us know about this issues. Just like on other issues like staingate and the butterflykeyboardgate, It is great that you report all this problems even if some people don’t like to hear about them.
Score: 9 Votes (Like | Disagree)
Populus Avatar
73 months ago

Thank you! I will not be buying anything that says M1 or M1x for at least 2 years.
Actually -and anyone who thinks I am wrong, please correct me- I think this threat is the same for Intel and M1 macs. It is compiled for both architectures.
Score: 8 Votes (Like | Disagree)